Managed SOC for businesses
We monitor your systems 24/7 from Palma, with our own technicians and no subcontracting.
Monitor before reacting; tools are not enough if nobody is watching them
Most SMEs hit by a cyberattack discover too late that the alerts were already there: in the EDR, in the firewall, in Microsoft 365 logs. Nobody saw them in time because nobody had the capacity to watch 24/7.
A managed SOC changes that order. Human shifts watching in real time, active containment when an incident is confirmed and traceable evidence that can support applicable NIS2, ISO 27001 or ENS measures. It is not a dashboard. It is a team behind the dashboard, operating from Spain, with our own technicians in Palma.
What a properly delivered managed SOC includes
24/7 monitoring
Uninterrupted monitoring across endpoints, network, cloud and email. There is always an analyst on the other side, not just automated alerts. Shifts covered by our own team in Palma, with no offshore subcontracting.
Managed detection and response
EDR/XDR deployment and management, with automatic containment when the playbook allows it and manual escalation to L2/L3 when the incident requires it. We act, we do not just notify.
SIEM management and threat hunting
Configuration, monthly tuning and continuous maintenance of SIEM (Microsoft Sentinel, Elastic, Wazuh) and firewall (Fortinet, WatchGuard, Sophos). Proactive search for indicators of compromise, not just reaction to alerts.
Reporting and evidence
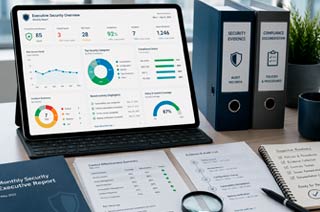
Monthly executive report for management with readable indicators and traceable technical evidence. It can support the risk and incident management covered by NIS2 Articles 21 and 23, according to the obligations and national framework applicable to the entity.
“DETECTION IS ONLY WORTH AS MUCH AS CONTAINMENT”
What changes after hiring a managed SOC in your company
Support for NIS2 incident response
Technical support to detect, analyse and document incidents and prepare applicable communications; the entity retains its notification responsibilities.
You gain real visibility
You know what is happening while it is happening, not when you discover it by chance.
You free up your IT team
Your IT team stops putting out fires after hours and focuses on projects.
You defend tenders
Monthly reporting and demonstrable SLAs for clients and public-sector bodies.
You reduce cost vs in-house
An in-house 24/7 SOC starts in six figures. A managed SOC turns it into a predictable fee.
You have a plan when it happens
Ransomware, data breach or fraud: protocol activated in minutes, not 48 hours.
‘Very professional. We’ve been working together for many years and will continue to do so for many more!’
Companies
that already trust us
Yes, these are some of our clients
Six signs of
a poorly set up managed SOC
If they are selling it to you by price, technology or vendor logo, they are selling you a dashboard. How to tell the difference.
They send alerts but do not contain
The service is run from another time zone
They do not integrate your cloud stack
Detection rules are not tuned
There is no executive reporting
They never put you to the test
When it makes sense
to hire a managed SOC
To support NIS2 incident management
For an entity subject to NIS2, Article 23 provides for an early warning without undue delay and no later than 24 hours after becoming aware of a significant incident, followed by further communications. A SOC can support detection, analysis and evidence preparation; it is not the only way to organise these functions and does not replace the entity’s responsibility or the applicable national framework.
When your IT team is at its limit
Your internal IT team already handles projects, support and supplier management. Asking them to also watch 24/7 is a recipe for burnout and missed alerts. A managed SOC unloads that layer without dismantling your team.
When a client or tender asks for evidence
Contracts with large accounts and public-sector bodies ask: “how do you monitor 24/7?”. Being able to attach monthly reporting and contractual SLAs is the difference between winning or losing the contract.
After an incident or serious attempt
Ransomware, CEO fraud or a data breach. A managed SOC can help detect and contain incidents earlier; no service can guarantee that all harm will be prevented.
How we work with a managed SOC step by step
Diagnosis and scope
- Initial 30–45 minute call to understand your infrastructure, regulatory obligations and sector. We define devices to monitor, integrations and SLAs. Written proposal with a fixed monthly price.
Onboarding (30–60 days)
- EDR/XDR deployment, SIEM integration with your sources (firewalls, cloud, identity, email), initial rule tuning and playbook definition. Onboarding determines the next two years.
Continuous operation
- 24/7 shifts, alert triage, active containment, proactive threat hunting and coordination with your internal IT. The same team that handled onboarding runs the operation.
Reporting and monthly review
- Executive report for management with business indicators. Rule review, risk profile update and adjustments based on threat evolution in your sector.
Exercises and continuous improvement
- Quarterly tabletop exercises with your team and an annual purple team exercise. The SOC stays alive; it does not stagnate in the first-day configuration.


FAQs
about Managed SOC
How much does a managed SOC cost?
The price depends on the monitored devices, integrations and contracted response level. After the assessment, we define the scope and provide a fixed quote.
What is the difference between managed SOC, MDR and SOCaaS?
The concepts overlap. A managed SOC outsources the full security operations center (team, processes, technology). MDR focuses on detection and response across endpoint and network, so it is more limited. SOCaaS is the commercial term for cloud-based SOC as a service. In practice they are used as synonyms: what matters is which SLAs are included and whether the provider contains or only notifies.
Will the SOC have access to our sensitive data?
The SOC accesses security logs, not the content of your data. Personal or confidential data does not leave your infrastructure unless a specific alert is forwarded for analysis. Processing is covered by a GDPR data processor agreement and NIS2 Article 21. SOC operated from Spain, not from third countries.
Do you subcontract the service?
No. We operate the SOC from Palma with our own in-house technicians. When a critical alert is triggered at 3 a.m., one of our analysts in Mallorca answers, not an offshore call-center operator.
Does a managed SOC help meet NIS2 requirements?
A SOC can support risk and incident management through detection, analysis, traceability and evidence preparation. Compliance depends on the full set of measures and obligations applicable to each entity, including the national framework. The service does not replace governance, policies, risk analysis or the entity’s responsibility for required communications.
What technology do you use?
Fortinet and WatchGuard for firewall/UTM, SentinelOne, Microsoft Defender for Business and Sophos for EDR/XDR, Microsoft Sentinel/Elastic/Wazuh for SIEM, Veeam for backup. We choose based on your existing stack and regulatory obligations.
How long does onboarding take?
Between 30 and 60 days depending on size and complexity. A small perimeter with standard cloud closes in 30 days; a multi-site environment with OT or custom integrations requires 60. We do not rush onboarding under pressure: a poorly tuned SOC creates noise for two years.
REQUEST A MANAGED SOC PROPOSAL
A 30-minute call is enough for us to define scope, answer questions and give you a realistic cost range.