ISO 27001 compliance for businesses

We implement your ISMS and support you through certification

We take you from gap analysis through to passing the certification audit with an ENAC-accredited body.

ISO 27001 Compliance for Businesses
Image 1
Image 2

ISO 27001 that works changes how the business operates

Most ISO 27001 projects that fail have the same origin: a folder with 80 documents and no real change in how the company operates. When the external audit arrives, the auditor looks at the process, not the template, and certification slips away.

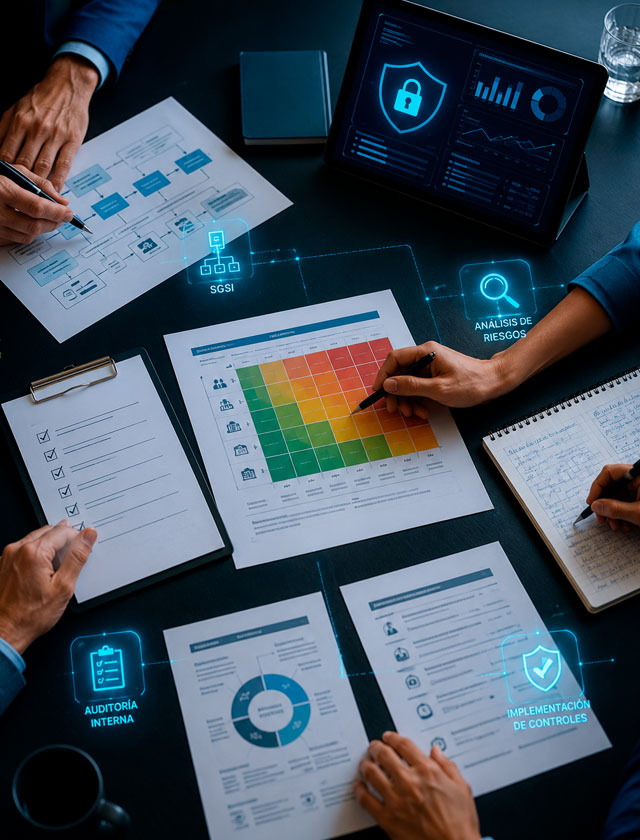
We do it the other way around. We implement an Information Security Management System (ISMS) that fits into real operations: risk analysis based on concrete assets, Annex A controls applied properly, traceable evidence and internal audits before the external audit so you arrive with margin. Most importantly, the work also serves NIS2, ENS and GDPR without duplicating effort.

What a properly delivered ISO 27001 implementation includes

ISO 27001 Compliance for Businesses

Gap analysis

Initial assessment against the requirements of ISO/IEC 27001:2022, the 2024 amendment and the 93 Annex A controls. We deliver a report showing what you already meet, what is missing and in what order to address it, with an effort estimate by phase.

ISO 27001 Compliance for Businesses

ISMS design and implementation

Definition of scope, security policy, risk analysis using the MAGERIT methodology, statement of applicability (SoA), operating procedures and assignment of responsibilities. A real ISMS integrated into operations, not a package of templates.

ISO 27001 Compliance for Businesses

Technical and organizational controls

Implementation of the Annex A controls that apply to your case: access management, cryptography, physical security, operations security, supplier management, continuity and regulatory compliance. Prioritized by risk, with a phased roadmap.

ISO 27001 Compliance for Businesses

Internal audit + certification support

Preliminary internal audit with our in-house ISO 27001 Auditor so you reach the external audit with margin. Support during the certification audit with an ENAC-accredited body (AENOR, BSI, Bureau Veritas, LRQA, DNV) and response to non-conformities.

“CERTIFICATION IS NOT DOCUMENTATION. IT IS PROOF THAT SOMETHING REALLY HAPPENS”

What changes after certifying ISO 27001 in your company

You win tenders and contracts

More and more corporate clients and public-sector bodies require ISO 27001 as an entry requirement. You stop losing opportunities because you do not have the certification.

You reduce due diligence friction

Answering security questionnaires from large clients goes from days to hours when the ISMS and SoA are ready.

You meet NIS2 and ENS with reusable work

70–80% of ISO 27001 work can be reused directly for NIS2, ENS and DORA. The investment pays off across several frameworks at once.

You lower your cyber insurance premium

Insurers recognize ISO 27001 as a maturity indicator. Lower premiums and better coverage with the same budget.

You organize real operations

Certification forces you to define processes, roles and metrics that improve efficiency beyond security. Operational benefit, not just regulatory value.

Documented management responsibility

Evidence that management took reasonable measures. Protection against claims after incidents that escalate into legal proceedings.

Companies
that already trust us

Yes, these are some of our clients

L'Arancina
Nautinort
Lionsgate Capital
Gallery Red
Rouge
Montis Advisors
Rosello
Cristalería Amanecer
Bufete Frau
Vectobal
esRadio Baleares
L'Arancina
Nautinort
Lionsgate Capital
Gallery Red
Rouge
Montis Advisors
Rosello
Cristalería Amanecer
Bufete Frau
Vectobal
esRadio Baleares

Six signs of
a poorly delivered ISO 27001 implementation

If the whole project boils down to 80 documents and a final PowerPoint, you are being sold a folder, not a system. How to tell the difference.

They promise “guaranteed certification”

No consultancy can guarantee certification because certification is issued by an independent body (AENOR, BSI, Bureau Veritas…) accredited by ENAC. Anyone who promises it either does not understand how the system works or is lying to you.

Nobody uses the ISMS after the project

They implement, certify and leave. If there is no trained internal owner and no continuous improvement plan, the next audit cycle will reveal that the ISMS is dead. And recertification will fail.

They copy generic templates without adapting them

Risk analysis with the same assets for every client. A SoA identical to your competitor’s. An experienced external auditor will detect it in ten minutes. It will not pass.

They do not work with the 2022 version and 2024 amendment

The current standard is ISO/IEC 27001:2022 with Amd 1:2024 (climate action). If the proposal refers to the 2013 or 2017 version, or does not mention the amendment, they are not up to date and are implementing against a standard that no longer applies.

They do not integrate NIS2, ENS or GDPR

Working on ISO 27001 without considering the regulatory context your company operates in means duplicating work in six months. A serious implementation integrates the applicable frameworks from the design stage, not at the end.

There is no in-house internal auditor

The internal audit requires independence. If the consultant who implements the system is the same person who audits it internally, that audit will not stand up for the external auditor. It is better to separate roles or use an ISO 27001 Auditor different from the project consultant.

When it makes sense
to certify in ISO 27001

01

When a client or tender requires it

Contracts with large accounts, public-sector bodies and regulated sectors ask for ISO 27001 as an entry requirement. Without the certificate, you do not pass the commercial filter. It is the #1 reason companies start the project.

02

To meet NIS2 with the least additional effort

ISO 27001 covers 70–80% of the technical and organizational requirements of NIS2 Article 21. If NIS2 applies to you, implementing ISO 27001 as part of a unified approach is cheaper and faster than doing it separately.

03

When you handle critical data or sensitive information

Healthcare (HIPAA / special-category GDPR data), financial, legal, technology businesses with intellectual property. Certification brings order to management and reduces the risk of incidents where reputational damage is greater than the technical damage.

04

As a B2B commercial strategy

Differentiation from uncertified competitors. Access to demanding international markets. Better negotiation with insurers. Clear ROI in long sales cycles with large accounts.

How we work through an ISO 27001 implementation step by step

ISO 27001 Compliance for Businesses
ONE
1

Diagnosis and proposal

TWO
2

Gap analysis and plan

THREE
3

ISMS design and implementation

FOUR
4

In-house internal audit

FIVE
5

Certification and maintenance

FAQs
about ISO 27001 compliance

It depends on the scope and size of the organization. Indicative range: from €8,000–25,000 for an SME with a limited scope, up to €15,000–40,000 for mid-sized companies with a cross-site scope. Certification body costs (AENOR, BSI…) are independent and usually range from €3,000–8,000 depending on size. We provide a fixed price by phase after the initial gap analysis.

It depends on your starting point. Between 3 and 6 months for an SME with a solid previous base, between 6 and 12 months for a mid-sized company with no prior management-system experience, and 12–18 months for large organizations with a cross-site scope. Add another 4–8 weeks for the external audit process and certificate issuance.

No consultancy can guarantee it because certification is issued by an independent external body accredited by ENAC. What we do guarantee is that you reach the external audit with the ISMS implemented and the preliminary internal audit passed. In projects we have handled this way, the first-audit success rate is very high, but the certificate is issued by the external auditor, not by us.

ISO/IEC 27001:2022 with Amd 1:2024 (which incorporates climate-action considerations). If your company is certified under previous versions (2013 or 2017), we also support your transition to the 2022 version.

Yes, very substantially. 70–80% of ISO 27001 work can be used directly for NIS2 (Article 21) and ENS. DORA has more nuance because it applies to financial entities with specific requirements, but the risk management and continuity base is reusable. If you know you will need to comply with several frameworks, the efficient approach is to implement them in a unified way from the start.

ISO 27001 is the certifiable standard; it contains the ISMS requirements. ISO 27002 is a good-practice guide for implementing ISO 27001 Annex A controls. It is not certifiable. Consultancies use both: 27001 defines what must be done; 27002 guides how to do it.

No. Our own team works from Palma: an in-house ISO 27001 Auditor, cybersecurity consultants and legal experts. The same team supports you from gap analysis through to recertification.

A 30-minute call is enough for us to define the scope, answer questions and give you a realistic cost range.