ENS compliance for businesses
We take you from categorization through to certification by an ENAC-accredited OAT. Royal Decree 311/2022, official CCN tools and work reusable for ISO 27001 and NIS2.
Adapting to ENS means proving real compliance in an audit
If you provide services to the Public Administration, ENS is a legal requirement. Without a declaration or certificate of compliance, you are left out of tenders and renewals, no matter how competitive your pricing is.
We work with the official CCN tools (PILAR, INES, CCN-STIC guides) and our own ISO 27001 auditor, who performs the internal audit before the external one. The work can be reused for ISO 27001 and NIS2.
What a properly executed ENS adaptation includes
Categorization and risk analysis
Low/Medium/High category according to the 5 ENS dimensions and risk analysis with PILAR, the official CCN tool.
Adaptation plan and statement of applicability
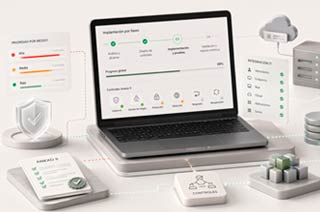
Security policy, timeline-based plan, Annex II statement of applicability and appointment of the Security Officer (RSI).
Implementation of technical and organizational measures
Annex II controls implemented in phases and prioritized by risk. Integrated with your IT, not layered on top of it.
Internal audit and OAT support
Internal audit with our own ISO 27001 Auditor, upload to INES and support during the external audit by the ENAC-accredited OAT.
“IN ENS, THE LEVEL IS NOT CHOSEN. IT IS CATEGORIZED”
What changes after certifying ENS in your company
You can tender with public administrations
Ministries, regional governments, city councils, universities and public healthcare.
You reduce time spent on tenders
Prepared documentation, without improvising for every call for tenders.
You comply with NIS2 by reusing work
70-80% of the ENS work can be reused directly for NIS2.
A natural bridge to ISO 27001
If you are aiming for the international certification, you already have half the work done.
Fewer serious incidents
ENS-certified organizations have a stronger real-world security posture.
Documented legal protection
Evidence of due diligence in the event of claims or incidents.
‘Very professional. We’ve been working together for many years and will continue to do so for many more!’
Companies
that already trust us
Yes, these are some of our clients
Six signs of
a poorly delivered ENS compliance project
If someone offers you a fast, cheap ENS process or suggests lowering the level to simplify it, they are selling you a future problem. How to spot it.
They propose Low to save money
They do not use CCN tools
They confuse Declaration with Certification
They work with RD 3/2010
They ignore specific compliance profiles
There is no plan after certification
When it makes sense
to adapt to ENS
You are going to tender with public administrations
Ministries, regional governments, city councils, universities, public healthcare. Without ENS, you do not pass the tender filter.
You are a critical supplier to a public body
ENS applies to you by contract, not because you choose it. Your client will require compliance in order to renew.
You want to reuse the work for NIS2 or ISO 27001
Working on the three standards in an integrated way is cheaper and faster than doing them separately. 70-80% of the work is shared.
How we work on ENS adaptation step by step
Categorization
- Preliminary categorization according to the 5 dimensions of Annex I and a fixed-price proposal by phase.
Risk analysis with PILAR
- Full analysis using the official CCN tool and Annex II statement of applicability.
Plan and implementation
- Policy, procedures, appointed RSI and controls implemented in risk-prioritized phases.
Internal audit and INES
- Internal audit with our own ISO 27001 Auditor and upload of the National Security Status Report.
Certification and maintenance
- Support during the audit by an ENAC-accredited OAT and annual follow-up until renewal.


FAQs
about ENS compliance
How much does ENS adaptation cost?
ENS Medium: €10,000-€30,000. ENS High: €20,000-€50,000. The OAT cost must be added to this (€3,000-€7,000 depending on category). Fixed price by phase after the initial categorization.
How long does it take?
ENS Medium: 6-12 months. ENS High: 12-18 months. Add 2-3 months for the external audit. Less time if you already have ISO 27001 or ENS from the previous version.
Declaration or Certification?
Low allows a Declaration of Compliance (self-declared). Medium and High require a Certificate of Compliance issued by an ENAC-accredited OAT.
What is the difference between ENS and ISO 27001?
ENS is a Spanish regulation for the public sector and its suppliers. ISO 27001 is a voluntary international standard. They share 70-80% of the work.
Does ENS help with NIS2 compliance?
To a large extent. ENS Medium or High covers the technical basis of Article 21 of NIS2. Article 23 deadlines and the supply chain still need to be reviewed.
Can I assign Low to simplify the process?
No. The category is determined by the dimensions applied to your system. Assigning it incorrectly can lead to the certificate being withdrawn during the audit.
Do you work with PILAR, INES and CCN-STIC?
Yes. They are the official CCN tools, and we use them in all our ENS adaptation projects.
REQUEST AN ENS ADAPTATION PROPOSAL
A 30-minute call is enough for us to categorize your system and give you a realistic cost range.